Nixpkgs security tracker

Try the new UI
Login with GitHub
⚠️ You are using a production deployment that is still only suitable for demo purposes. Any work done in this might be wiped later without notice.

Dismissed suggestions

These automatic suggestions were dismissed after initial triaging.

to select a suggestion for revision.

View:
Compact
Detailed
Dismissed
(max. allowed matches exceeded)
Permalink CVE-2026-89894
7.8 HIGH
  • CVSS version (CVSS): 3.1
  • Attack Vector (AV): Local (L)
  • Attack Complexity (AC): Low (L)
  • Privileges Required (PR): Low (L)
  • User Interaction (UI): None (N)
  • Scope (S): Unchanged (U)
  • Confidentiality (C): High (H)
  • Integrity (I): High (H)
  • Availability (A): High (H)
  • Modified Attack Vector (MAV): Local (L)
  • Modified Attack Complexity (MAC): Low (L)
  • Modified Privileges Required (MPR): Low (L)
  • Modified User Interaction (MUI): None (N)
  • Modified Confidentiality (MC): High (H)
  • Modified Scope (MS): Unchanged (U)
  • Modified Integrity (MI): High (H)
  • Modified Availability (MA): High (H)
created 1 week, 4 days ago Activity log
  • Created & dismissed (max. allowed matches exceeded) suggestion
media: cx231xx: reject geometry changes while the VBI queue is busy

In the Linux kernel, the following vulnerability has been resolved: media: cx231xx: reject geometry changes while the VBI queue is busy vidioc_s_fmt_vid_cap() and vidioc_s_std() change the device-wide dev->width / dev->norm but only refuse the change when the *video* queue (dev->vidq) is busy. The VBI queue (dev->vbiq) shares that same geometry: cx231xx_init_vbi_isoc() latches dma_q->lines_per_field from dev->norm, the VBI videobuf2 plane is sized from dev->width / dev->norm in vbi_queue_setup() and vbi_buf_prepare(), and cx231xx_do_vbi_copy() then recomputes the destination offset from the *live* dev->width and the latched lines_per_field on every URB completion: offset = lines_completed * (dev->width << 1) + ...; if (dma_q->current_field == 2) offset += dev->width * 2 * dma_q->lines_per_field; memcpy(plane + offset, p_buffer, lencopy); Because the VBI node shares video_ioctl_ops with the video node, an application can size a small VBI plane (REQBUFS/QBUF with a small width, or with the NTSC standard), then enlarge dev->width (or switch dev->norm to PAL) through the video node while the VBI stream is running -- the change is allowed because only dev->vidq is checked -- and let the device deliver a field-2 VBI payload. cx231xx_do_vbi_copy() now computes the offset with the larger geometry and memcpy()s past the end of the smaller plane that was already allocated, a heap out-of-bounds write whose offset is attacker-chosen and whose contents come from the device. The per-field guard in cx231xx_copy_vbi_line() does not help: it bounds the copy against the latched lines_per_field, not the plane's real capacity, and vb2 does not re-run buf_prepare() for an already prepared buffer. Refuse the format/standard change when the VBI queue is busy as well, so the geometry cannot change underneath an allocated VBI buffer.

Affected products

Linux
  • =<7.2.*
  • <627a121c15fe05a541f44d86016294b80bada75d
  • <90d50648af36a1fbf5dbc99238de6fd0e58a13e0
  • <aa3314506deb9703bcf0e889db08959440228fbf
  • <a636c72c7f522d984fa498fc0631f33a2d0be3fd
  • ==5.5
  • <5.5
  • =<6.12.*
  • <a5dd3d7fba358ff9486f3f51b2a9038348c0970a
  • <54ac6df8b8d97eddc3ae97fd2045bdedc8541b6d
  • =<5.15.*
  • =<6.18.*
  • <7087bef6510c7df5df0b19192633b8ecc0f33a6f
  • =<*
  • =<6.1.*
  • =<6.6.*
  • =<5.10.*
  • <1d1079db8d1807e259a1d2679ed314949797aad9
Dismissed
(no matching packages found)
Permalink CVE-2026-11984
5.3 MEDIUM
  • CVSS version (CVSS): 3.1
  • Attack Vector (AV): Network (N)
  • Attack Complexity (AC): Low (L)
  • Privileges Required (PR): None (N)
  • User Interaction (UI): None (N)
  • Scope (S): Unchanged (U)
  • Confidentiality (C): Low (L)
  • Integrity (I): None (N)
  • Availability (A): None (N)
  • Modified Attack Vector (MAV): Network (N)
  • Modified Attack Complexity (MAC): Low (L)
  • Modified Privileges Required (MPR): None (N)
  • Modified User Interaction (MUI): None (N)
  • Modified Confidentiality (MC): Low (L)
  • Modified Scope (MS): Unchanged (U)
  • Modified Integrity (MI): None (N)
  • Modified Availability (MA): None (N)
created 1 week, 4 days ago Activity log
  • Created & dismissed (no matching packages found) suggestion
Ad Inserter <= 2.8.16 - Missing Authorization to Unauthenticated Header/Footer Code Disclosure via 'ai-debug-code' Parameter

The Ad Inserter – Ad Manager & AdSense Ads plugin for WordPress is vulnerable to authorization bypass in all versions up to, and including, 2.8.16 due to a missing capability check on the `ai-debug-code` URL-parameter. This makes it possible for unauthenticated attackers to view administrator-configured header and footer code blocks that have been disabled from public display.

Affected products

Ad Inserter – Ad Manager & AdSense Ads
  • =<2.8.16
Dismissed
(no matching packages found)
Permalink CVE-2026-90843
5.5 MEDIUM
  • CVSS version (CVSS): 4.0
  • Attack Vector (AV): Network (N)
  • Attack Complexity (AC): Low (L)
  • Attack Requirement (AT): None (N)
  • Privileges Required (PR): None (N)
  • User Interaction (UI): None (N)
  • Vulnerable System Impact Confidentiality (VC): Low (L)
  • Vulnerable System Impact Integrity (VI): Low (L)
  • Vulnerable System Impact Availability (VA): Low (L)
  • Subsequent System Impact Confidentiality (SC): Low (L)
  • Subsequent System Impact Integrity (SI): Low (L)
  • Subsequent System Impact Availability (SA): Low (L)
  • Exploit Maturity (E): POC (P)
  • Modified Attack Vector (MAV): Network (N)
  • Modified Attack Complexity (MAC): Low (L)
  • Modified Attack Requirement (MAT): None (N)
  • Modified Privileges Required (MPR): None (N)
  • Modified User Interaction (MUI): None (N)
  • Modified Vulnerable System Impact Confidentiality (MVC): Low (L)
  • Modified Vulnerable System Impact Integrity (MVI): Low (L)
  • Modified Vulnerable System Impact Availability (MVA): Low (L)
  • Modified Subsequent System Impact Confidentiality (MSC): Low (L)
  • Modified Subsequent System Impact Integrity (MSI): Low (L)
  • Modified Subsequent System Impact Availability (MSA): Low (L)
  • Safety (S): Not Defined (X)
  • Automatable (AU): Not Defined (X)
  • Recovery (R): Not Defined (X)
  • Value Density (V): Not Defined (X)
  • Vulnerability Response Effort (RE): Not Defined (X)
  • Provider Urgency (U): Not Defined (X)
  • Confidentiality Req. (CR): Not Defined (X)
  • Integrity Req. (IR): Not Defined (X)
  • Availability Req. (AR): Not Defined (X)
created 1 week, 4 days ago Activity log
  • Created & dismissed (no matching packages found) suggestion
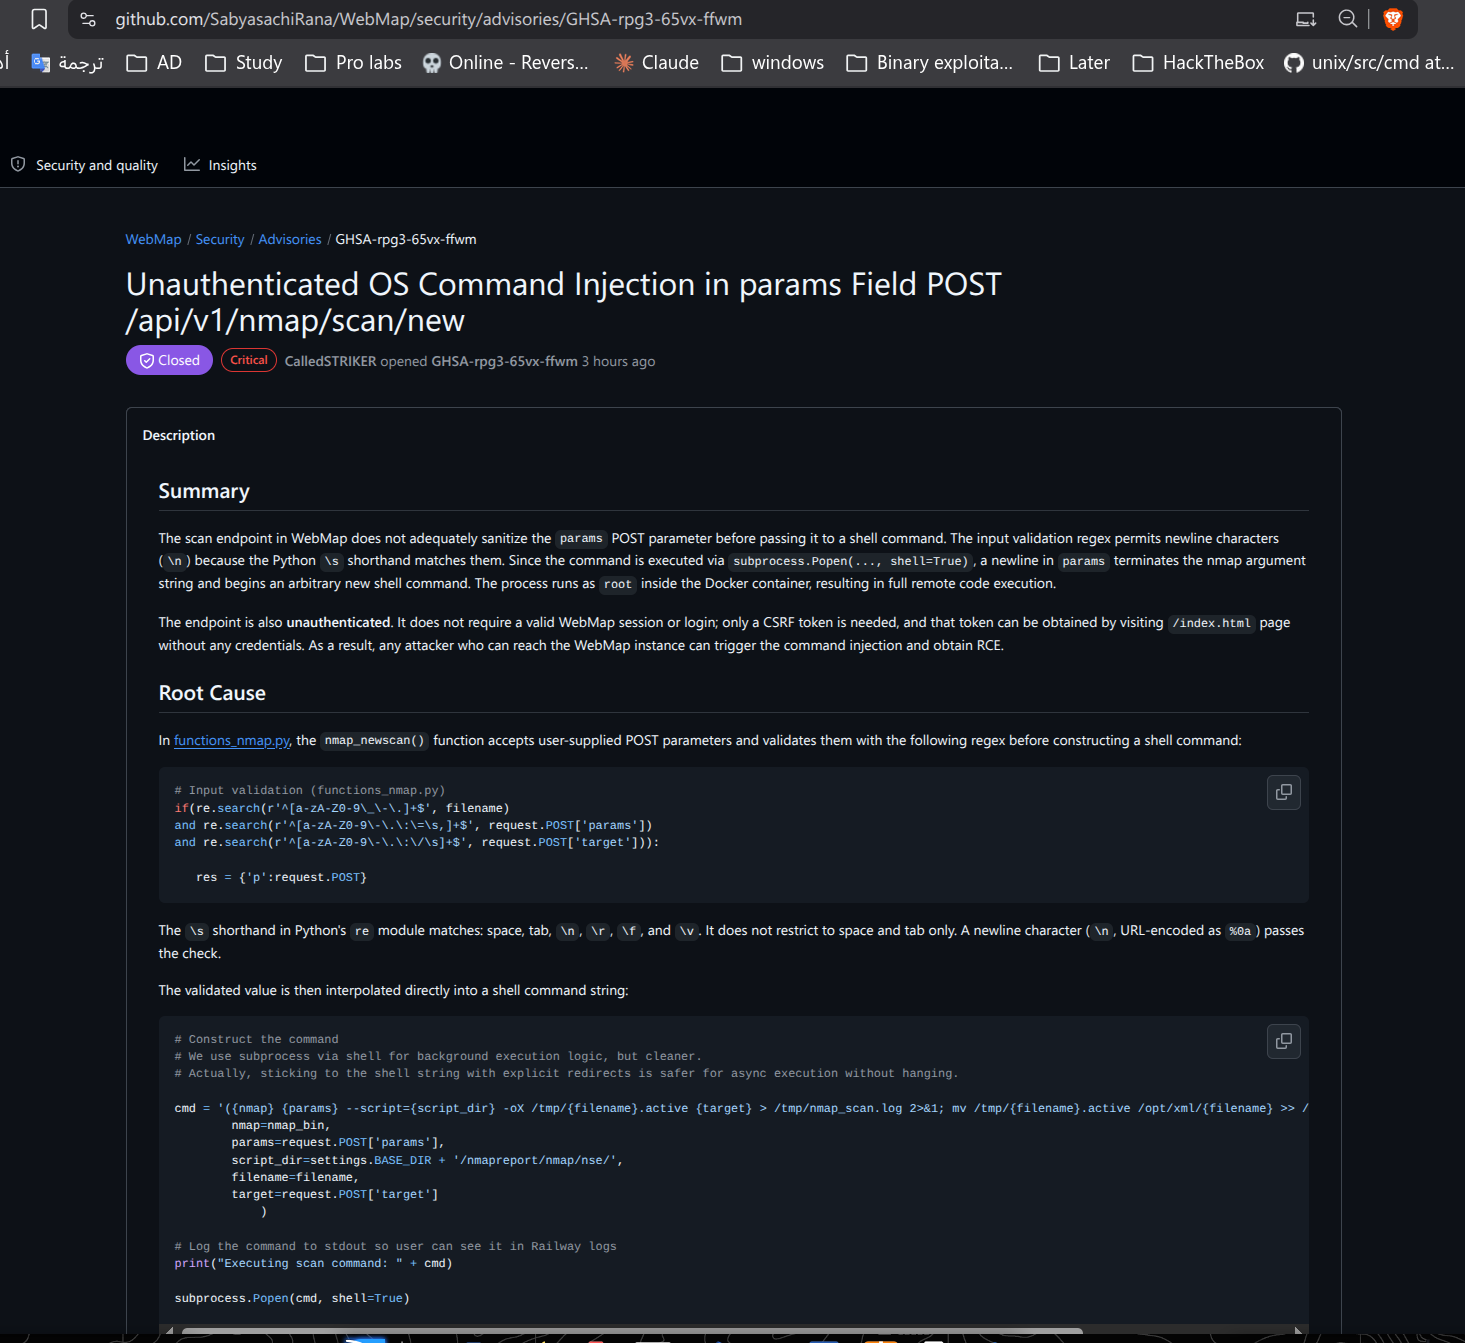
SabyasachiRana WebMap New Nmap Scan functions_nmap.py nmap_newscan os command injection

A security vulnerability has been detected in SabyasachiRana WebMap up to 8b95fe4dc301a3c09ddf145b895de0bf9f8d2a25. This affects the function nmap_newscan of the file functions_nmap.py of the component New Nmap Scan Handler. Such manipulation of the argument target/params leads to os command injection. The attack may be launched remotely. The exploit has been disclosed publicly and may be used. The name of the patch is 3d52f65803a2716bff14d938352c6fef45b0cfb6. A patch should be applied to remediate this issue. This issue got fixed with a silent patch.

Affected products

WebMap
  • ==8b95fe4dc301a3c09ddf145b895de0bf9f8d2a25
Dismissed
(no matching packages found)
created 1 week, 4 days ago Activity log
  • Created & dismissed (no matching packages found) suggestion
Rox Appointment Booking < 1.2.8 - Unauthenticated Internal Notes Disclosure via Service and Category REST Routes

The Rox Appointment Booking WordPress plugin before 1.2.8 does not perform any authorization check on the endpoints that return booking service and category records, allowing unauthenticated attackers to read the private internal notes stored on each service and category.

References

Affected products

Rox Appointment Booking
  • <1.2.8
Dismissed
(no matching packages found)
Permalink CVE-2026-92380
5.5 MEDIUM
  • CVSS version (CVSS): 4.0
  • Attack Vector (AV): Network (N)
  • Attack Complexity (AC): Low (L)
  • Attack Requirement (AT): None (N)
  • Privileges Required (PR): None (N)
  • User Interaction (UI): None (N)
  • Vulnerable System Impact Confidentiality (VC): Low (L)
  • Vulnerable System Impact Integrity (VI): Low (L)
  • Vulnerable System Impact Availability (VA): Low (L)
  • Subsequent System Impact Confidentiality (SC): None (N)
  • Subsequent System Impact Integrity (SI): None (N)
  • Subsequent System Impact Availability (SA): None (N)
  • Exploit Maturity (E): POC (P)
  • Modified Attack Vector (MAV): Network (N)
  • Modified Attack Complexity (MAC): Low (L)
  • Modified Attack Requirement (MAT): None (N)
  • Modified Privileges Required (MPR): None (N)
  • Modified User Interaction (MUI): None (N)
  • Modified Vulnerable System Impact Confidentiality (MVC): Low (L)
  • Modified Vulnerable System Impact Integrity (MVI): Low (L)
  • Modified Vulnerable System Impact Availability (MVA): Low (L)
  • Modified Subsequent System Impact Confidentiality (MSC): Negligible (N)
  • Modified Subsequent System Impact Integrity (MSI): Negligible (N)
  • Modified Subsequent System Impact Availability (MSA): Negligible (N)
  • Safety (S): Not Defined (X)
  • Automatable (AU): Not Defined (X)
  • Recovery (R): Not Defined (X)
  • Value Density (V): Not Defined (X)
  • Vulnerability Response Effort (RE): Not Defined (X)
  • Provider Urgency (U): Not Defined (X)
  • Confidentiality Req. (CR): Not Defined (X)
  • Integrity Req. (IR): Not Defined (X)
  • Availability Req. (AR): Not Defined (X)
created 1 week, 4 days ago Activity log
  • Created & dismissed (no matching packages found) suggestion
WuzhiCMS Remote Image Fetch index.php saveRemote server-side request forgery

A flaw has been found in WuzhiCMS up to 4.1.0. The impacted element is the function ckditor::saveRemote of the file coreframe/app/attachment/index.php of the component Remote Image Fetch. This manipulation of the argument source[] causes server-side request forgery. The attack can be initiated remotely. The exploit has been published and may be used. The project was informed of the problem early through an issue report but has not responded yet.

Affected products

WuzhiCMS
  • ==4.1.0
  • ==4.0
Dismissed
(no matching packages found)
created 1 week, 4 days ago Activity log
  • Created & dismissed (no matching packages found) suggestion
Formidable Forms 6.34 - Unauthenticated Stored Content Injection via 'updated_by' Parameter

The Formidable Forms WordPress plugin before 6.35 does not restrict who can set the identifier recording which user last edited a form entry, and relies on that identifier when deciding whether to strip HTML from stored entry values, allowing unauthenticated visitors to have markup rendered in the admin entry view that would otherwise be removed, and to attribute their submission to an administrator who never made it.

References

Affected products

Formidable Forms
  • <6.35
Dismissed
(no matching packages found)
Permalink CVE-2026-91843
9.8 CRITICAL
  • CVSS version (CVSS): 3.1
  • Attack Vector (AV): Network (N)
  • Attack Complexity (AC): Low (L)
  • Privileges Required (PR): None (N)
  • User Interaction (UI): None (N)
  • Scope (S): Unchanged (U)
  • Confidentiality (C): High (H)
  • Integrity (I): High (H)
  • Availability (A): High (H)
  • Modified Attack Vector (MAV): Network (N)
  • Modified Attack Complexity (MAC): Low (L)
  • Modified Privileges Required (MPR): None (N)
  • Modified User Interaction (MUI): None (N)
  • Modified Confidentiality (MC): High (H)
  • Modified Scope (MS): Unchanged (U)
  • Modified Integrity (MI): High (H)
  • Modified Availability (MA): High (H)
created 1 week, 4 days ago Activity log
  • Created & dismissed (no matching packages found) suggestion
Stack overflow in login process to the Security Management and Log Servers

A stack overflow during the unauthenticated login process may allow an attacker to run arbitrary code remotely with root privileges.

Affected products

Quantum Security Management
  • ==R80.20 (EOS)
  • ==R80.30 (EOS)
  • ==R80.40 (EOS)
  • ==R81.10 (EOS) with Jumbo Hotfix Take 190 or below
  • ==R82.10 with Jumbo Hotfix Take 44 or below
  • ==R80.10 (EOS)
  • ==R81 (EOS)
  • ==R80 (EOS)
  • ==R81.20 with Jumbo Hotfix Take 166 or below
  • ==R82 with Jumbo Hotfix Take 126 or below
Dismissed
(no matching packages found)
Permalink CVE-2026-79651
7.5 HIGH
  • CVSS version (CVSS): 3.1
  • Attack Vector (AV): Network (N)
  • Attack Complexity (AC): Low (L)
  • Privileges Required (PR): None (N)
  • User Interaction (UI): None (N)
  • Scope (S): Unchanged (U)
  • Confidentiality (C): None (N)
  • Integrity (I): None (N)
  • Availability (A): High (H)
  • Modified Attack Vector (MAV): Network (N)
  • Modified Attack Complexity (MAC): Low (L)
  • Modified Privileges Required (MPR): None (N)
  • Modified User Interaction (MUI): None (N)
  • Modified Confidentiality (MC): None (N)
  • Modified Scope (MS): Unchanged (U)
  • Modified Integrity (MI): None (N)
  • Modified Availability (MA): High (H)
created 1 week, 4 days ago Activity log
  • Created & dismissed (no matching packages found) suggestion
Keycloak-services: keycloak-services: unauthenticated dos via unbounded locale caching

A flaw was found in the theme localization endpoints of the keycloak-services component, which is the core service responsible for authentication flows and theme management in Keycloak. The issue occurs because the system accepts arbitrary locale tags from unauthenticated requests and stores them in a permanent in-memory cache without limits. An attacker can exploit this by sending a large number of unique locale tags, eventually causing the server to run out of memory and crash.

References

Affected products

keycloak-services
rhbk/keycloak-rhel9
  • *
rhbk/keycloak-rhel9-operator
  • *
keycloak/rhbk-openshift-rhel9
rhbk/keycloak-operator-bundle
  • *
Dismissed
(no matching packages found)
Permalink CVE-2026-86108
7.5 HIGH
  • CVSS version (CVSS): 4.0
  • Attack Vector (AV): Network (N)
  • Attack Complexity (AC): High (H)
  • Attack Requirement (AT): None (N)
  • Privileges Required (PR): High (H)
  • User Interaction (UI): None (N)
  • Vulnerable System Impact Confidentiality (VC): High (H)
  • Vulnerable System Impact Integrity (VI): High (H)
  • Vulnerable System Impact Availability (VA): High (H)
  • Subsequent System Impact Confidentiality (SC): None (N)
  • Subsequent System Impact Integrity (SI): None (N)
  • Subsequent System Impact Availability (SA): None (N)
  • Modified Attack Vector (MAV): Network (N)
  • Modified Attack Complexity (MAC): High (H)
  • Modified Attack Requirement (MAT): None (N)
  • Modified Privileges Required (MPR): High (H)
  • Modified User Interaction (MUI): None (N)
  • Modified Vulnerable System Impact Confidentiality (MVC): High (H)
  • Modified Vulnerable System Impact Integrity (MVI): High (H)
  • Modified Vulnerable System Impact Availability (MVA): High (H)
  • Modified Subsequent System Impact Confidentiality (MSC): Negligible (N)
  • Modified Subsequent System Impact Integrity (MSI): Negligible (N)
  • Modified Subsequent System Impact Availability (MSA): Negligible (N)
  • Safety (S): Not Defined (X)
  • Automatable (AU): Not Defined (X)
  • Recovery (R): Not Defined (X)
  • Value Density (V): Not Defined (X)
  • Vulnerability Response Effort (RE): Not Defined (X)
  • Provider Urgency (U): Not Defined (X)
  • Confidentiality Req. (CR): Not Defined (X)
  • Integrity Req. (IR): Not Defined (X)
  • Availability Req. (AR): Not Defined (X)
  • Exploit Maturity (E): Not Defined (X)
created 1 week, 4 days ago Activity log
  • Created & dismissed (no matching packages found) suggestion
Security Advisory 0181

Insufficient validation of inputs supplied through affected VeloCloud Edge management and configuration workflows may allow an authorized management request or configuration value to be interpreted as an operating-system command. Successful exploitation may allow command execution with elevated privileges on the affected VeloCloud Edge.

References

Affected products

VeloCloud Edge
  • =<5.2.6.x
  • <5.2.0
  • =<6.4.1.x
  • =<6.1.4.x
Dismissed
(no matching packages found)
created 1 week, 4 days ago Activity log
  • Created & dismissed (no matching packages found) suggestion
Xpro Elementor Addons < 1.7.9 - Contributor+ Stored XSS via Interactive Circle Widget

The Xpro Addons — 140+ Widgets for Elementor WordPress plugin before 1.7.9 does not validate or sanitize a widget link setting before storing and using it in a JavaScript navigation call, allowing users with the contributor role and above to inject and store JavaScript that executes in the browser of anyone who interacts with the affected widget.

References

Affected products

Xpro Addons — 140+ Widgets for Elementor
  • <1.7.9