 Nixpkgs security tracker
Dismissed
(no matching packages found)
Permalink
CVE-2026-90843
5.5 MEDIUM
- CVSS version (CVSS): 4.0
- Attack Vector (AV): Network (N)
- Attack Complexity (AC): Low (L)
- Attack Requirement (AT): None (N)
- Privileges Required (PR): None (N)
- User Interaction (UI): None (N)
- Vulnerable System Impact Confidentiality (VC): Low (L)
- Vulnerable System Impact Integrity (VI): Low (L)
- Vulnerable System Impact Availability (VA): Low (L)
- Subsequent System Impact Confidentiality (SC): Low (L)
- Subsequent System Impact Integrity (SI): Low (L)
- Subsequent System Impact Availability (SA): Low (L)
- Exploit Maturity (E): POC (P)
- Modified Attack Vector (MAV): Network (N)
- Modified Attack Complexity (MAC): Low (L)
- Modified Attack Requirement (MAT): None (N)
- Modified Privileges Required (MPR): None (N)
- Modified User Interaction (MUI): None (N)
- Modified Vulnerable System Impact Confidentiality (MVC): Low (L)
- Modified Vulnerable System Impact Integrity (MVI): Low (L)
- Modified Vulnerable System Impact Availability (MVA): Low (L)
- Modified Subsequent System Impact Confidentiality (MSC): Low (L)
- Modified Subsequent System Impact Integrity (MSI): Low (L)
- Modified Subsequent System Impact Availability (MSA): Low (L)
- Safety (S): Not Defined (X)
- Automatable (AU): Not Defined (X)
- Recovery (R): Not Defined (X)
- Value Density (V): Not Defined (X)
- Vulnerability Response Effort (RE): Not Defined (X)
- Provider Urgency (U): Not Defined (X)
- Confidentiality Req. (CR): Not Defined (X)
- Integrity Req. (IR): Not Defined (X)
- Availability Req. (AR): Not Defined (X)
Activity log
- Created & dismissed (no matching packages found) suggestion
SabyasachiRana WebMap New Nmap Scan functions_nmap.py nmap_newscan os command injection
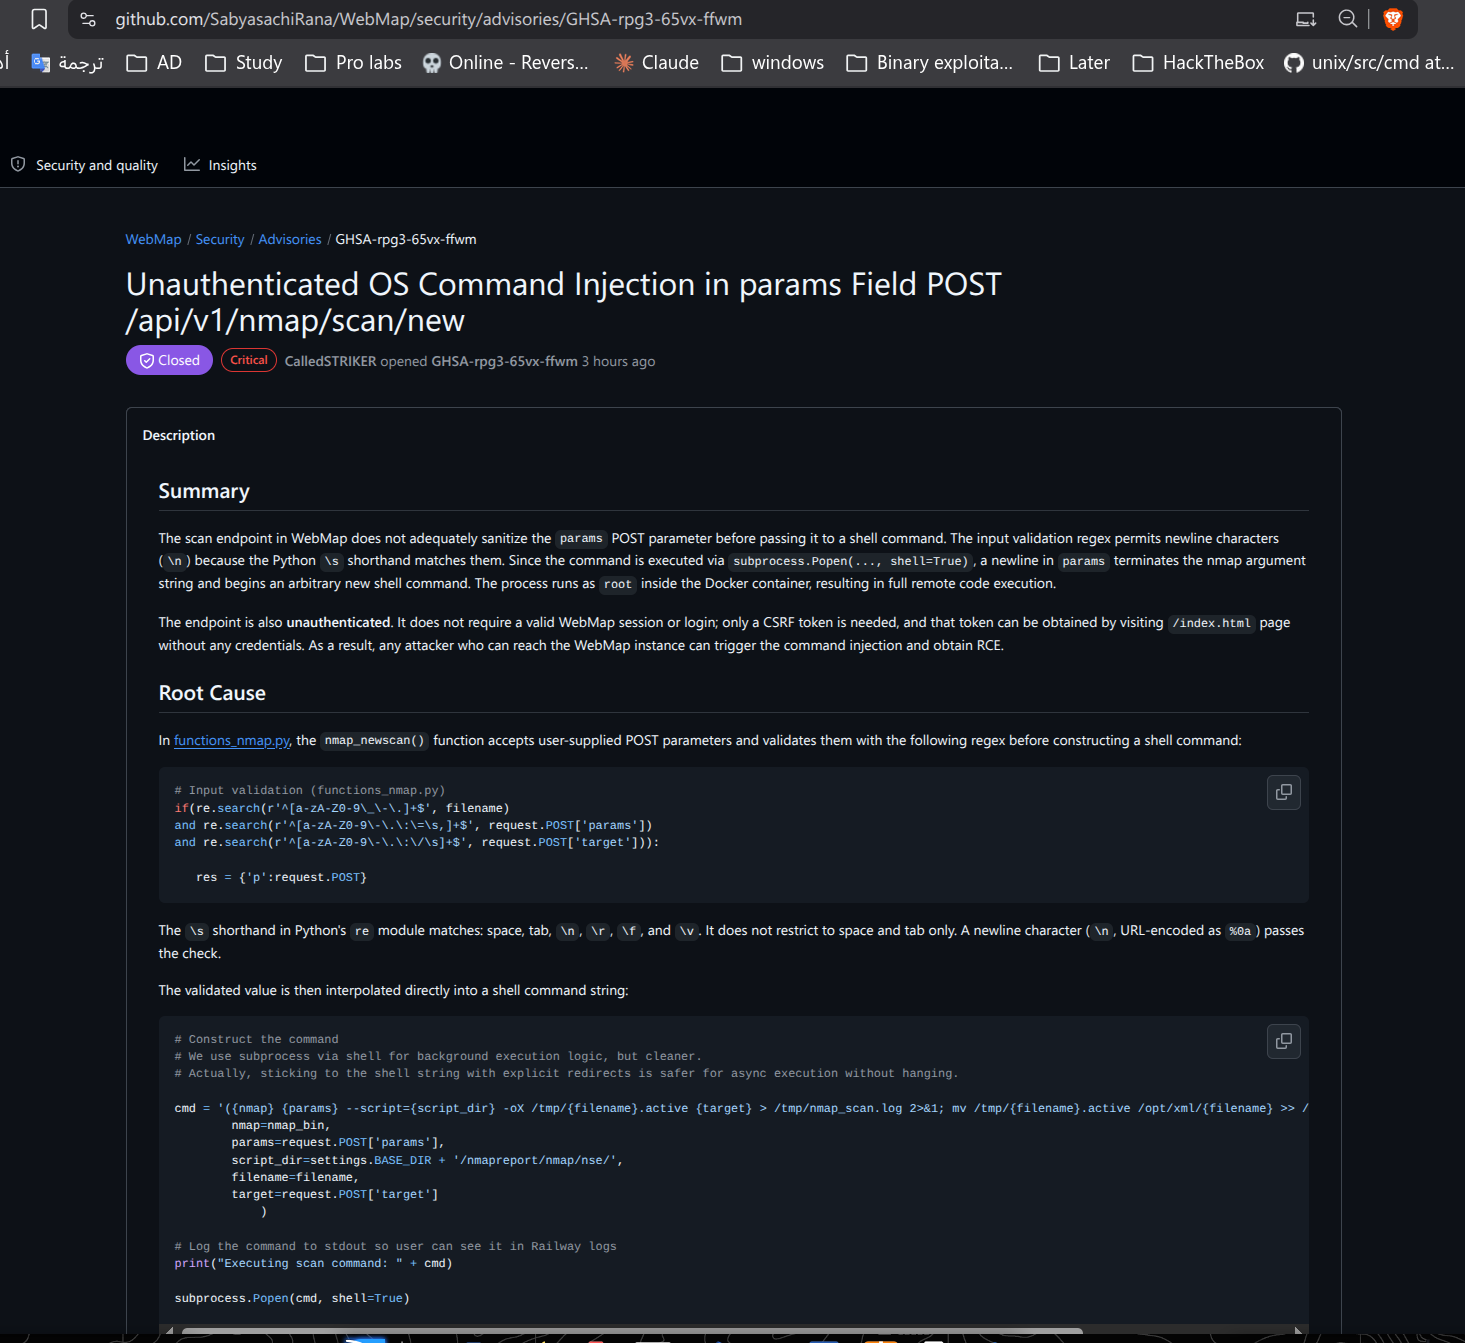
A security vulnerability has been detected in SabyasachiRana WebMap up to 8b95fe4dc301a3c09ddf145b895de0bf9f8d2a25. This affects the function nmap_newscan of the file functions_nmap.py of the component New Nmap Scan Handler. Such manipulation of the argument target/params leads to os command injection. The attack may be launched remotely. The exploit has been disclosed publicly and may be used. The name of the patch is 3d52f65803a2716bff14d938352c6fef45b0cfb6. A patch should be applied to remediate this issue. This issue got fixed with a silent patch.
References
-
VDB-403395 | SabyasachiRana WebMap New Nmap Scan functions_nmap.py nmap_newscan os command injection vdb-entrytechnical-description
-
-
CVE-2026-90843 | CVE Analysis and Report third-party-advisory
-
Affected products
WebMap
- ==8b95fe4dc301a3c09ddf145b895de0bf9f8d2a25